
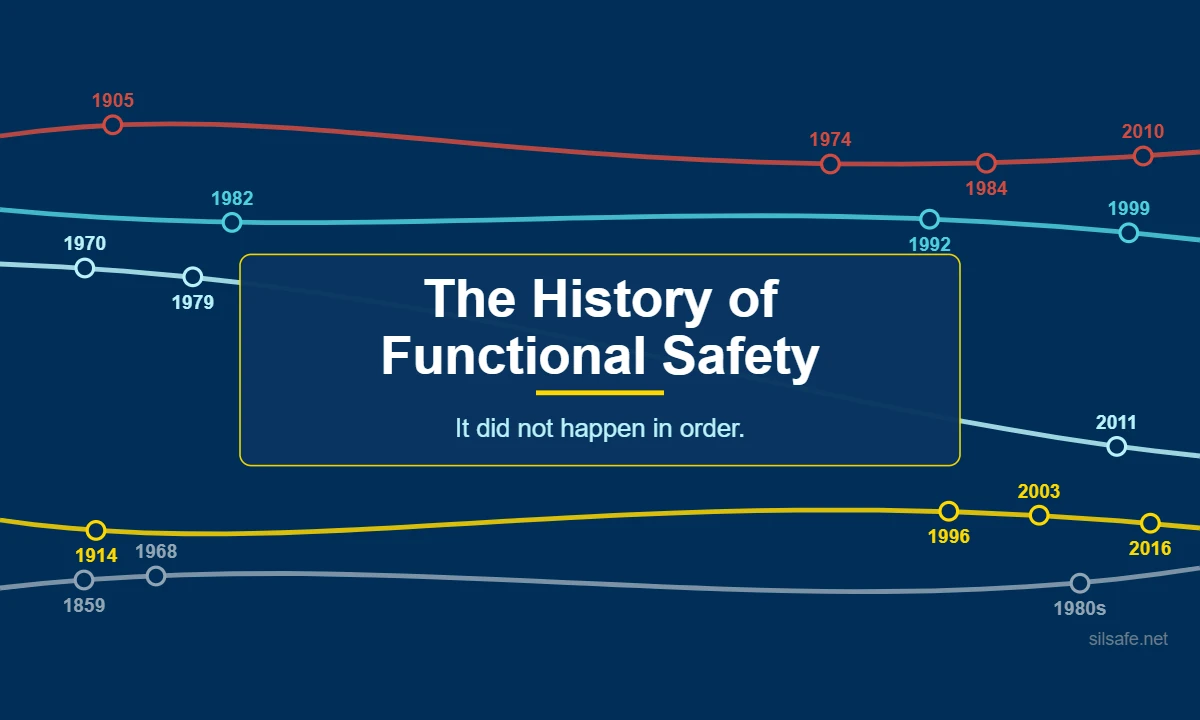
The history of functional safety reads like a sequence in most tellings. An accident happens, a regulator responds, a committee writes a standard, and industry complies. It is a tidy story, it is easy to teach, and it is how most people first meet functional safety.
That sequence is wrong in its particulars and wrong in its shape. The accidents, the rulemaking, the committee fights, and the hardware were all in motion at the same time, and each was reacting to the others mid-stride.
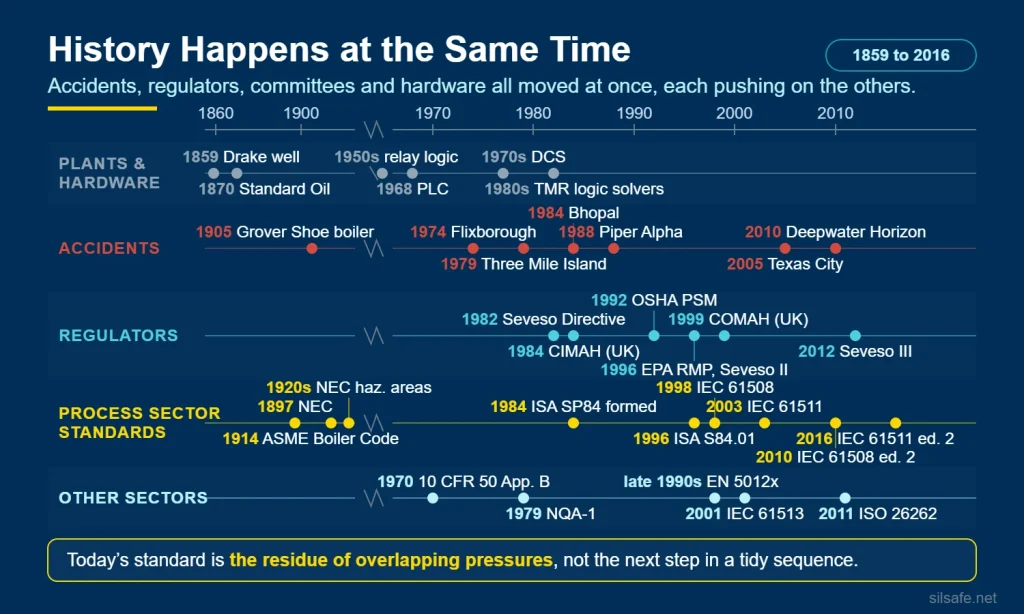
The ISA panel that produced the first process sector standard was commissioned in 1984. That is the same year as Bhopal, within a decade of both Three Mile Island and the first European major-accident directive, and right as the first triple modular redundant safety controllers were reaching the market. Every one of those is usually told as its own episode, with its own cause and its own consequence. They were happening at once.
The Oil Industry Grew Faster Than Anyone Could Make It Safe
Commercial oil production in the US began with the Drake well at Titusville, Pennsylvania in 1859, and refining capacity followed within a few years with almost no engineering consensus behind it. John D. Rockefeller’s Standard Oil consolidated a fragmented industry from 1870, so scale arrived long before any shared understanding of how to contain what was being processed.
Early refineries ran on open flames, riveted vessels, and manual valves. Fires and boiler failures were a routine cost of operation rather than an exceptional event, and they were priced in the way spoilage is priced in.
Signs reading “smokers will be shot” were posted at refinery and tank farm sites, a detail recorded in Ron Chernow’s Titan. They tell you both how severe the ignition hazard was and how little else was available to manage it. The hazard was real enough: at Goose Creek, Texas in 1917, several oil tanks burned after a lit cigarette was thrown down.
What Counted as Protection in an Early Refinery
Protection in this era meant a human being watching a gauge and operating a valve, supplemented by mechanical devices that needed no intelligence to act.
Relief valves, rupture discs, and fusible links had already been invented, and they worked because they responded to the physics directly, with no measurement, no logic, and no decision. The pressure relief valve in particular long predates the oil industry. Denis Papin fitted one to his steam digester around 1679, and the design matured through railway and boiler service across the 1800s. Refinery-specific relief practice was not codified until API RP 520 in 1955, nearly three centuries later.
Everything else was the operator. He was the instrument, the logic solver, and the final element at once, which is functional safety with no engineering behind it, and the integrity of the protection was the integrity of that person’s attention.
The First Real Codes Came From Electricity and Boilers
Electricity got there first. UK wiring rules appeared in 1882, NFPA’s sprinkler rules in 1896, and the National Electrical Code in 1897, all before any boiler construction code existed.
The Boiler Code
Boiler explosions were killing people at a rate that made them a public policy problem rather than an industrial one. The Grover Shoe Factory disaster in Brockton, Massachusetts in March 1905 killed 58 people and turned that into legislation.
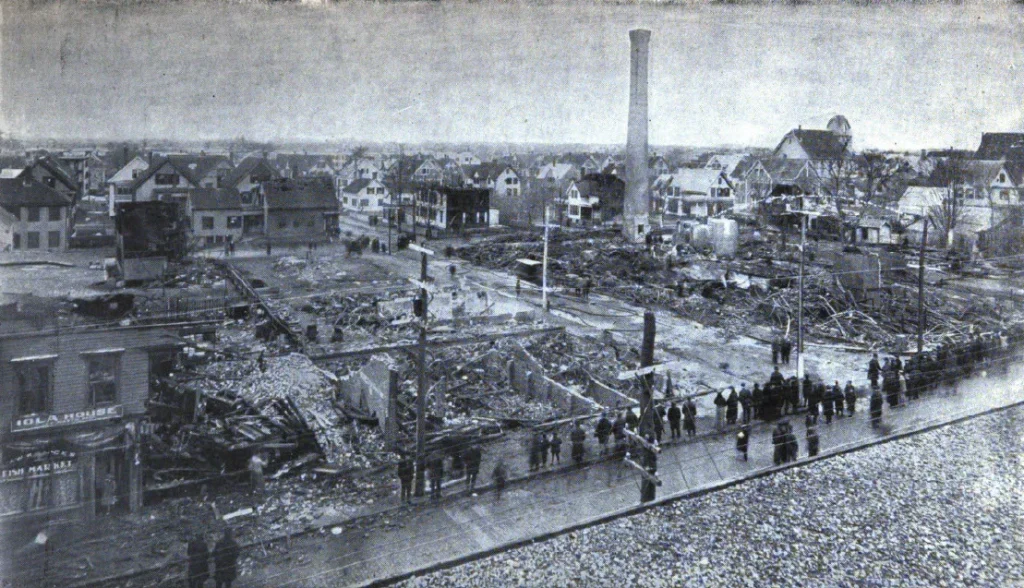
Massachusetts created a Board of Boiler Rules and published its boiler laws in 1908. The patchwork of state rules that followed pushed industry toward a single national code.
ASME was founded in 1880, formed its Boiler Code Committee in 1911, and published the first Boiler and Pressure Vessel Code (BPVC), the 1914 edition, in 1915. ASME had issued a boiler testing code as early as 1884, but that measured performance rather than governing safe construction, which is a different job.
The BPVC established the pattern functional safety still follows. A consensus committee writes the engineering requirement, and jurisdictions adopt it by reference. Nothing about that arrangement has changed in a hundred years.
Hazardous Area Classification
The 1920 National Electrical Code introduced the first hazardous location rules, under the label “extra hazardous locations,” because all electrical work was then considered hazardous and these places were worse. The Class scheme followed in 1931, Divisions in 1947, and Zones in 1996, and the rules continue to evolve today.
Hazardous area classification is not a safety instrumented system and does not behave like one. But it is one of the oldest pieces of process safety practice still in daily use, and it constrains the instruments and final elements a safety instrumented function can be built from.
Processes Outran the People Watching Them
Refining and chemical processing grew through the mid-century into continuous, high-throughput, tightly heat-integrated plants that no longer behaved slowly enough for a human to intervene reliably.
Higher pressures, larger inventories, exothermic chemistry, and tighter integration all shortened the time available between an upset and a loss of containment. The operator who had been the whole protective system was now being asked to respond inside windows that no operator could consistently hit.
Protective automation emerged to cover the gap, beginning with pneumatic interlocks and hardwired relay logic that tripped the process without waiting for a decision. This is the problem functional safety exists to solve, decades before it had a name.
Microprocessors Rewrote What Protection Could Be
The relay dates to telegraphy around 1835, and protective relays reached power systems by the early 1900s, so relay logic was mature technology long before anyone applied it to process trips. No first relay trip on a process plant could be determined for this article, and that is probably not an archival gap. Interlocks were routine plant engineering rather than product launches, so nobody wrote one down as a first.
The programmable logic controller (PLC) was specified in 1968 and the first units shipped in 1969. Plant logic then migrated out of physical wiring over decades rather than years, with relay-based protective systems remaining in service long after programmable equipment existed. Plenty of them still are.
August Systems, founded in the UK in 1978, first proved three microprocessors could carry out a single valid control action, building on aerospace majority-voting work. Triconex followed, shipping its first Tricon in 1986.
Software introduced a failure mode relay logic did not have. A systematic fault reproduces identically in every redundant channel, which hardware voting cannot correct. Three processors running the same flawed logic all reach the same wrong answer at the same moment, confidently and in agreement. Much of what functional safety now requires of software follows from that single property.
The Accidents Moved Faster Than the Standards
A handful of accidents are routinely named as the reason functional safety exists. The relationship is messier than that.
Flixborough in the UK killed 28 people in June 1974, and the Advisory Committee on Major Hazards was set up before the year was out.
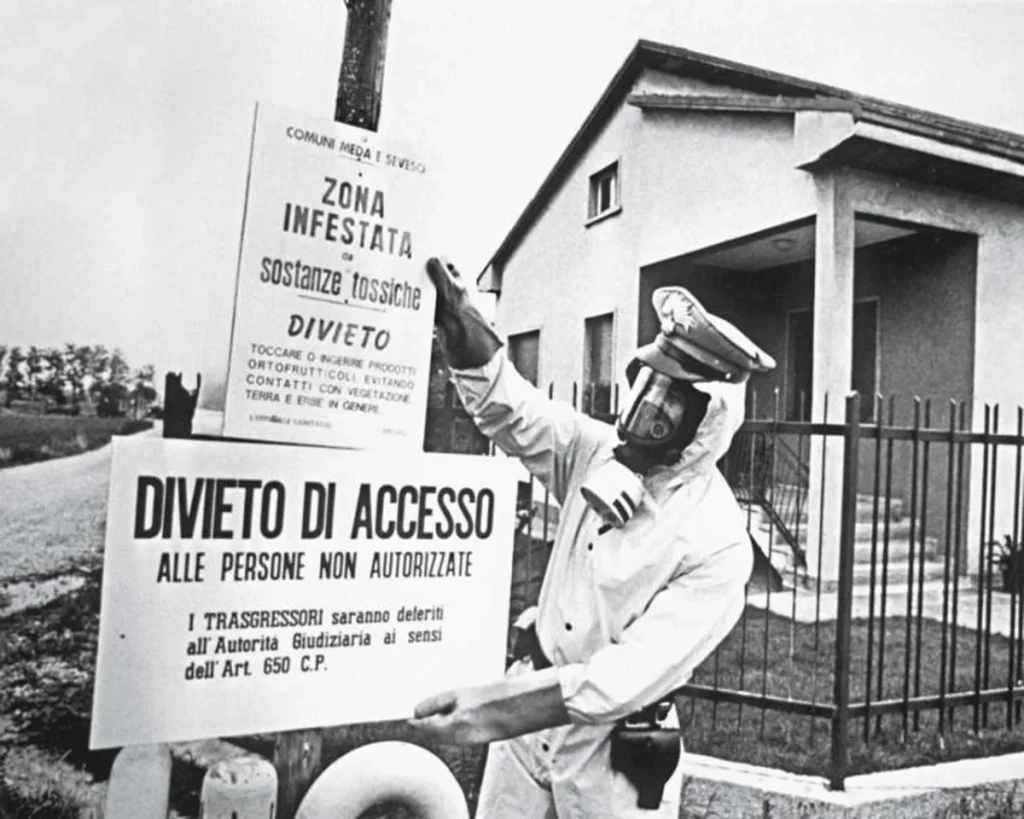
Seveso in Italy in July 1976 released a dioxin cloud with no immediate deaths. The plant was actually at Meda. The directive took the name of the town worst affected by the exposure, which is a persistent source of confusion, including for the author of this article.
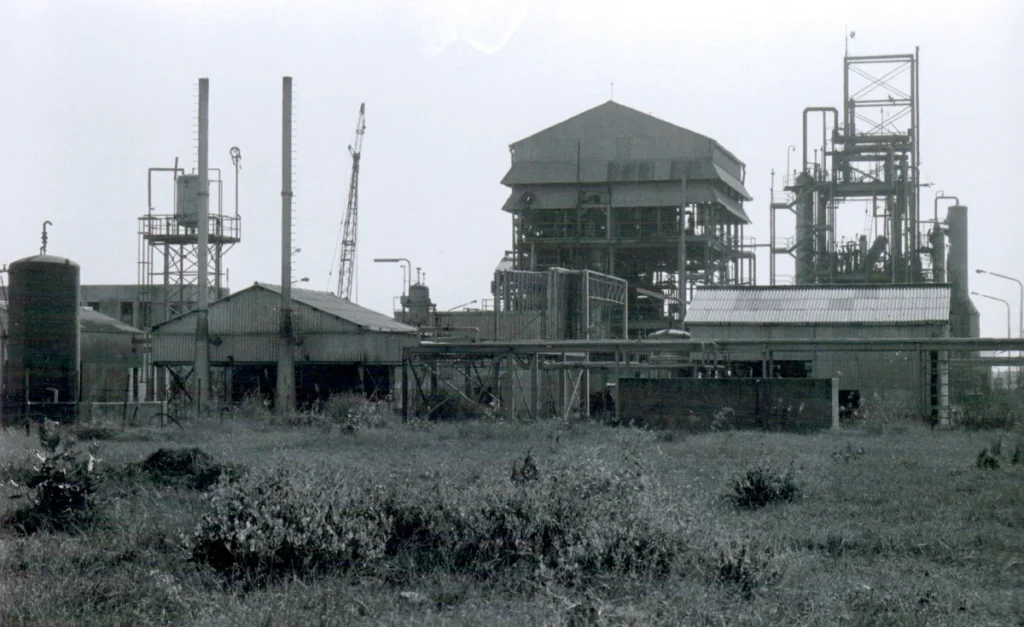
Bhopal in India in December 1984 has no authoritative death toll. Government compensation records, state surveys, and OSHA’s own rulemaking background range from about 2,000 to over 15,000, and that disagreement is itself part of the history.
Piper Alpha killed 167 men in the North Sea in July 1988. Cullen reported in 1990, offshore safety moved to the Health and Safety Executive (HSE) in 1991, and the safety case regulations followed in 1992.
Phillips Pasadena in Texas killed 23 people in October 1989 and is routinely described as the cause of US process safety management. OSHA’s own background lists it alongside Bhopal, BASF Cincinnati, and IMC Sterlington, so it was one cited driver rather than the sole one.
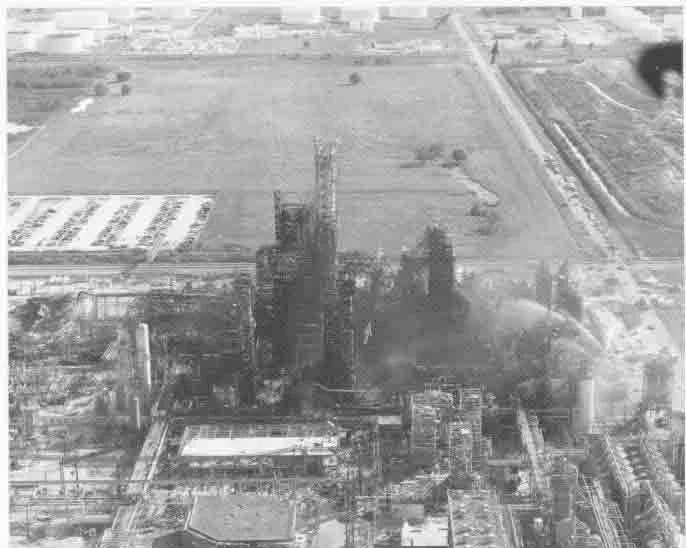
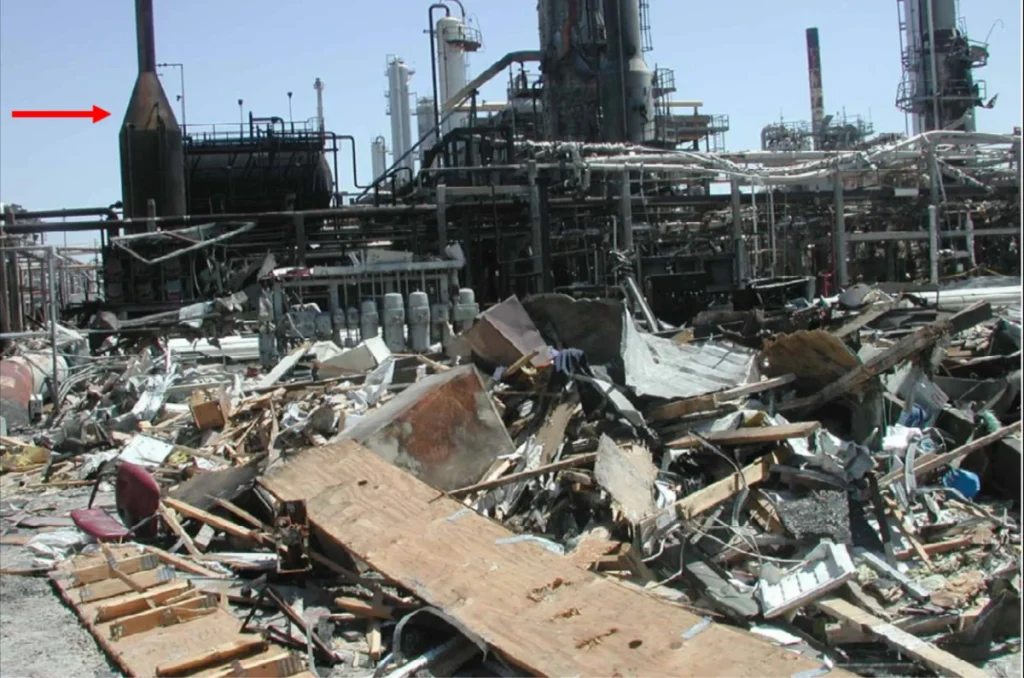
BP Texas City killed 15 in March 2005, the first of three accidents in this list to arrive after the standards already existed.
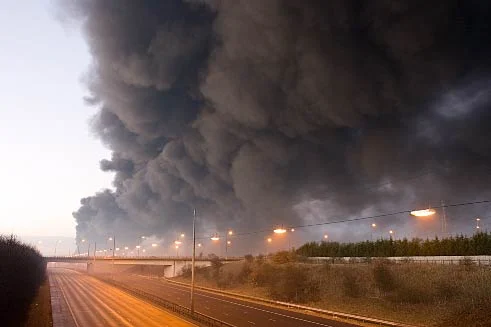
Buncefield in the UK in December 2005 has the most direct functional safety link of any accident here. An independent high-level switch failed to operate because its test arm had not been locked. The official follow-up called for a common method of setting integrity requirements for overfill protection under BS EN 61511-3, which is a regulator pointing at the functional safety standard by name.
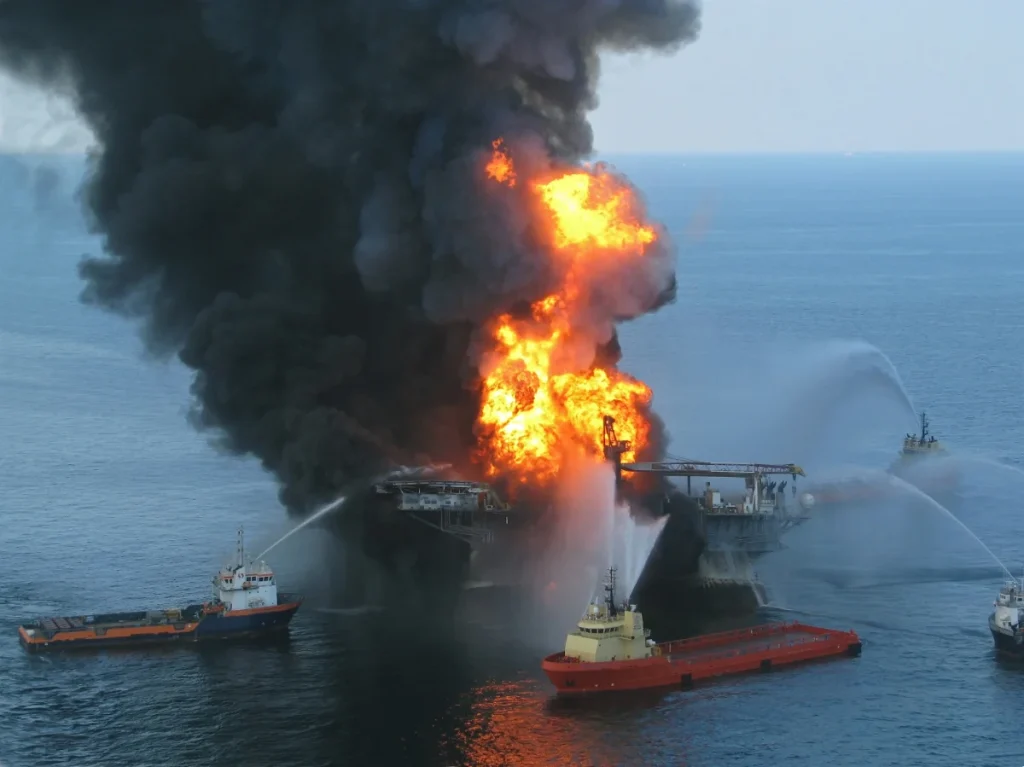
Deepwater Horizon killed 11 in the Gulf of Mexico in April 2010. The offshore safety rule that followed had already closed its comment period before the blowout, so the accident accelerated a rule rather than starting one.
Regulators Worked the Same Problem in Parallel
Europe Got There First
The Seveso Directive was adopted in June 1982, succeeded by Seveso II in December 1996 and Seveso III in July 2012.
The UK identified hazardous sites under NIHHS in 1982, implemented Seveso through CIMAH in December 1984, and replaced it with COMAH in 1999, built around a safety case and a demonstration that risk is as low as reasonably practicable.
CIMAH is dated the day after Bhopal and is often read as a response to it. It implements a directive adopted two years earlier and was drafted well before the release. The dates line up; the causation does not.
European major-accident regulation preceded the equivalent US rules by roughly a decade.
United States
OSHA proposed the Process Safety Management rule, 29 CFR 1910.119, in July 1990, issued it in February 1992, and it took effect in May 1992. Its requirement to follow recognized and generally accepted good engineering practice became the hook that pulls consensus standards into enforceable territory.
The EPA Risk Management Program rule followed in June 1996 under the Clean Air Act Amendments of 1990, covering offsite consequence rather than worker exposure.
OSHA wrote to ISA in 2000 recognising ISA 84 as good engineering practice under the mechanical integrity clause. That is how a voluntary standard acquired regulatory weight without ever being incorporated by reference.
Adoption Beyond Europe and the United States
CENELEC, the European standards body for electrotechnical work, published EN 61511-1 in December 2004, identical to IEC 61511:2003, and national editions followed across Europe from there.
Gulf operators appear to have taken IEC 61511 up largely through company engineering standards and contract requirements rather than national law, making the route commercial rather than regulatory. The relevant national oil company standards are proprietary, so this is a reading of how the work reaches site rather than a documented fact. A national oil company that also sets the rules for its own sector produces a different compliance dynamic than an independent regulator does.
China issued the GB/T 21109 series from 2007. GB/T is China’s national standards designation, with the T marking it as a recommended rather than mandatory standard, and the series is the Chinese adoption of IEC 61511. Australia adopted the IEC 61511 parts as AS standards. Functional safety adoption travelled through national standards bodies rather than through a single global mandate.
Two Regulatory Philosophies
European regulation asks the operator to demonstrate adequacy while US regulation asks the operator to comply with requirements, and that difference still shows up in how functional safety work is scoped and documented on either side.
ISA 84, IEC 61508, and IEC 61511
The Twelve-Year Argument

ISA Standards Panel 84 was commissioned in 1984 and worked under the title “Programmable Electrical-Electronic Systems for Use in Safety Applications,” which is a reminder that the vocabulary we now use did not exist when the work started.
ANSI/ISA-S84.01 was published in February 1996, twelve years after the panel was commissioned. That gap is the single most revealing fact about how contested the work was.
The committee spent those years deadlocked between two ideas of what a standard is. A prescriptive design standard tells the engineer what to build. A performance-based standard sets a target and requires the engineer to demonstrate it has been met.
The prescriptive approach failed for two reasons. Equipment vendors lobbied for their own hardware to be the prescribed answer, which made agreement impossible. And end users with unusual chemistry could demonstrate that prescribed solutions were unsafe in their service, which made agreement undesirable.
The performance-based outcome is why functional safety requires calculation and verification rather than a lookup table. That choice, made out of deadlock, shaped everything that followed.
CCPS published Guidelines for Safe Automation of Chemical Processes in 1993, while the panel was still deadlocked, and it used the term safety interlock system, abbreviated SIS. ISA 84 committee members objected that interlocks described only one subset of safety-related systems, and the same three letters were later redefined as safety instrumented system. ISA used the book as a key drafting reference. The acronym is older than the words it now stands for.
How the Three Standards Fit Together
The IEC set up a task group on a generic standard for programmable electronic systems in September 1985, one year after the ISA panel was commissioned, so the two efforts overlapped almost from the start.
They were separate efforts by separate bodies rather than joint drafting, but ISA worked with sight of the IEC drafts. S84.01 contains a formal annex comparing itself against the 1995 IEC draft, and after publishing it the ISA 84 committee turned to supporting IEC 61508 and IEC 61511, reviewing the process sector standard throughout its development.
IEC 61508 appeared in stages. Parts 1, 3, 4, and 5 were approved in 1998 and Parts 2, 6, and 7 not until February 2000.
IEC 61511:2003 took the foundational approach of IEC 61508 and applied it to the process sector, and it was already a named IEC project before its parent was finished. The 1999 final draft of IEC 61508-2 calls IEC 61511 the proposed process-sector implementation and tells US and Canadian users to apply ANSI/ISA-S84.01-1996 until it publishes.
The division of labour is what that relationship means in practice. IEC 61508 governs the manufacturer who builds and certifies a device. IEC 61511 governs the end user who selects those devices and integrates them into a system for a process application.
ANSI/ISA-S84.01 stopped at safety integrity level (SIL) 3 because the committee judged SIL 4 impractical to design and imprudent to rely on. IEC 61508 and IEC 61511 acknowledge SIL 4 and warn against designing one.
What ISA 84 Means Today
ANSI/ISA-84.00.01-2004 adopted IEC 61511:2003 in September 2004, identical except for a grandfather clause lifted from the OSHA rule.
ANSI/ISA-61511-1/2/3-2018 replaced it with an identical adoption of IEC 61511:2016+AMD1:2017. Since 2018 the US designation has been ANSI/ISA-61511, and the 84.00.01 number is retired.
No standalone S84 system design standard exists. The 84 number survives on the committee’s other products, including the ANSI standards 84.91.01 and 84.91.03 and a series of technical reports.
A practitioner who says they work to ISA 84 today almost always means IEC 61511 as adopted in the US, which is a different claim than it would have been in 1998.
IEC 61511 and the Guidance Around It
CCPS published Layer of Protection Analysis as a concept book in October 2001, written by industry practitioners rather than a standards committee. It has never been a standard.
IEC 61511-3 listed LOPA among its informative methods for determining required safety integrity levels. That is how an industry book became the default worldwide approach without ever becoming mandatory.
CCPS was still extending the method a decade later, publishing further LOPA guidance in 2013 and 2014.
When Did the First Safety Instrumented System Exist?
Hardwired emergency shutdown systems were doing the job of a safety instrumented function (SIF) decades before the term existed, with an instrument, a logic element, and a final element arranged to take the process to a safe state.
They were not all relay logic. Solid-state safety systems were in service through the 1960s, and HIMA’s Planar, the controller for what is described as the first process industry emergency shutdown system, was certified by TÜV in 1970. Certified programmable safety logic arrived in 1986, with HIMA’s H50 and the first Triconex Tricon shipping the same year.
What those systems lacked was not function but evidence. No required integrity target, no failure rate data, no verification that the arrangement achieved what it was credited with. Evidence is the part functional safety added.
The vocabulary came from outside the process sector entirely. HSE introduced a graded level of safety integrity in 1987 guidance on programmable electronic systems, and the UK Ministry of Defence published the first numbered levels, S1 to S4, in its 1991 interim defence standards. That is five years before the process sector had a standard at all.
So the standard did not invent the safety instrumented system. It defined what one has to demonstrate before it can be called one.
Failure Rate Data Moved From Experience to Certification
Early functional safety verification had almost no certified devices available, so engineers justified failure rates through prior use and proven in use arguments built on operating history at their own sites.
Prior use put the burden on the end user to show that the device had performed in comparable service. That favoured large operators with long maintenance records and disadvantaged everyone else, which meant the quality of a SIL verification depended partly on how good your site’s records happened to be.
Third-party certification of safety logic long predates IEC 61508 and ran against German standards first. TÜV certified HIMA’s Planar in 1970 and its first programmable system in 1986, under the DIN and VDE scheme rather than anything international. Products carried both the German AK ratings and IEC 61508 SILs through the 2000 to 2001 transition, and the earliest explicit IEC 61508 product claim found for this article is a field transmitter certified in June 2001.
Failure modes, effects and diagnostic analysis (FMEDA) gave manufacturers a route to publish quantified failure rates, and third-party certification turned that into a purchasable attribute. The UK’s CASS framework for assessing conformity to IEC 61508 began as a government initiative in 1998.
The proportion of safety instrumented systems built entirely from certified devices has risen steadily, to the point that specifying a certified device is now the default and prior use is the exception that has to be argued for.
Prior use never disappeared but is used less and less. It remains the only route for devices and services where no certified option exists.
Safety Software Became Its Own Problem
ANSI/ISA-S84.01-1996 had no software section, because protective logic was still predominantly hardwired and what software existed was treated as an extension of the hardware.
IEC 61511:2003 introduced a software clause, drawing the distinction between full variability languages used by device manufacturers and the limited variability languages used by end users configuring a logic solver.
IEC 61511:2016 simplified the software requirements, reflecting a decade of experience that most end user application programming is configuration rather than development.
Software failures are systematic rather than random, which is why the standard treats them through process and competence requirements instead of failure rate numbers. You cannot calculate your way out of a logic error, which is why this corner of functional safety looks so different from the rest of it.
Functional Safety Spread Beyond the Process Industry
IEC 61508 was written as a generic parent standard, and the functional safety sector standards that descend from it adapted its core to very different risk profiles.
- Automotive. ISO 26262:2011 replaced safety integrity levels with automotive safety integrity levels and reoriented the framework around vehicles produced in volume, with a second edition in 2018.
- Rail. The EN 5012x series developed from EN 50126-1 in 1999, covering reliability and safety management, software, and system safety approval, and has since consolidated the software parts into EN 50716:2023.
- Machinery. IEC 62061:2005 and ISO 13849-1 govern a world where demand on the protective function is continuous or high rather than the low demand typical of process plant.
- Nuclear. IEC 61513, first published in 2001, is maintained by a different IEC subcommittee and cross-refers to IEC 61508 rather than deriving from it the way IEC 61511 does.
The process sector branch diverged because its functions sit idle for years and are called on rarely, which is why probability of failure on demand became its governing measure.
Nuclear Took a Different Route
The nuclear industry arrived at rigorous safety requirements earlier than the process industry, and by a mechanism that is not functional safety at all: controlling quality of work and documentation rather than calculating the performance of a protective function.
10 CFR 50 Appendix B, a US federal regulation, established quality assurance requirements for safety-related nuclear work in 1970, more than two decades before process safety management existed in that country. It was programmatic rulemaking driven by a surge in reactor orders, not a response to an accident.
ANSI N45.2, published in 1971, was the quality assurance standard for nuclear power plants that Appendix B made necessary, and the N45 series is still referenced in nuclear work today. ASME NQA-1 was issued in 1979, consolidating that N45.2 series. ASME had taken the work on in 1975, so NQA-1 had been in development for four years by the time it published.
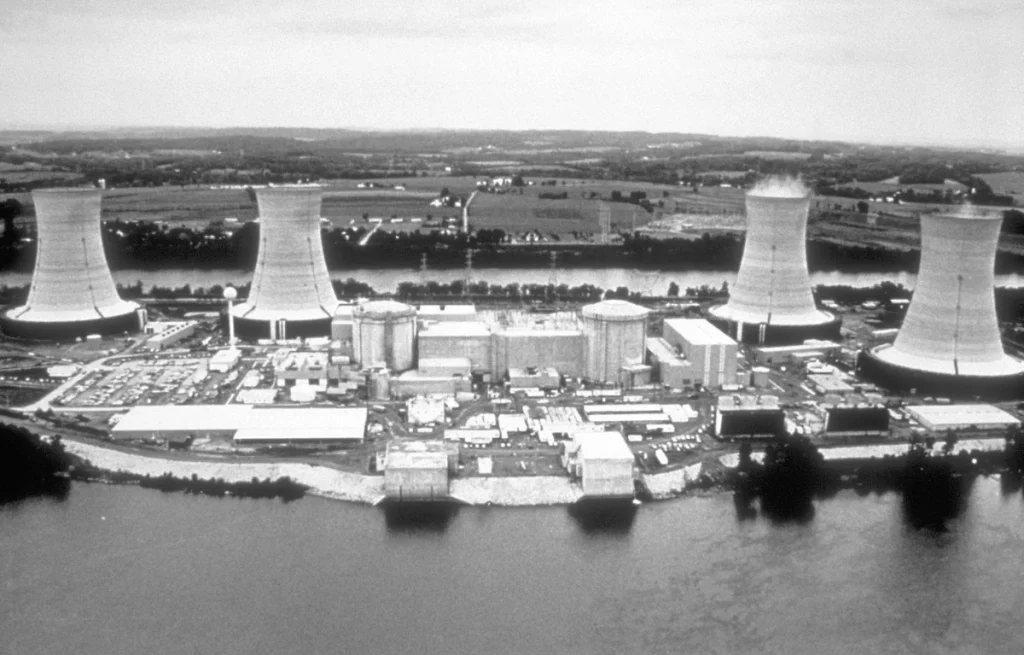
Three Mile Island happened in March 1979, the same year NQA-1 published, and the two are routinely linked. No evidence suggests the accident shaped the published text.
IEC 61513 gives nuclear an international instrumentation and control standard that cross-refers to IEC 61508. Its first edition published in March 2001, two years ahead of IEC 61511:2003, with a second edition in 2011 and a third in development. It is used in practice in Europe and in countries following IEC and IAEA convention. Finland’s regulator applies it directly and Russia has adopted it nationally, while US practice works to NRC regulation and IEEE standards.
IEC 61511 excludes nuclear facilities. Yet the management, documentation, and competence requirements NQA-1 imposed in 1979 anticipate requirements 61511 did not adopt until much later.
The Discipline Professionalized
Functional safety competence moved from an assumed attribute of an experienced engineer to a documented requirement. IEC 61511:2016 added formal procedures for managing it rather than leaving it presumed.
The first third-party personnel certification scheme launched in 2000 and TÜV Rheinland’s functional safety programme followed in 2004, creating a credential market where none had existed. ISA and UL have both added their own certificate programmes more recently, ISA’s built around the 61511 standard with the Automation Standards Compliance Institute.
Certification spread to the supply chain in parallel, with manufacturers, integrators, and assessment bodies carrying it as a commercial requirement rather than a technical one.
Independent functional safety assessment was built into the safety life-cycle by IEC 61508 in 1998, with assessor independence scaling to the consequence of getting it wrong. IEC 61511:2016 set it out in more detail.
Grandfathering Let Existing Plants Keep Running
The grandfather clause began as an American addition. ANSI/ISA-84.00.01-2004 adopted IEC 61511:2003 unchanged except for a grandfather provision lifted from the OSHA rule, and the international standard did not carry one.
IEC 61511:2016 brought it into the standard itself. Where a safety instrumented system was built to practices predating the standard, the user has to determine that it is designed, maintained, inspected, tested, and operating in a safe manner (5.2.5.4).
The standard applies the label retrospectively. A 1980s trip system was called an emergency shutdown system, an interlock, or a safety system at the time. The clause treats it as a “safety instrumented system” anyway, so there is something to apply the requirement to.
The determination is conditional and has to be documented. Facilities routinely treat the clause as a permanent exemption instead, which is the most common way this goes wrong.
Operating Plants Became the Hard Part
The standard’s early centre of gravity was design, and the industry discovered design was the easy half.
Proof testing, demand recording, and failure tracking turn design assumptions into claims that can be checked, and most facilities find the operating data does not match what was assumed. First edition calculations commonly assumed a proof test found everything. IEC 61511:2016 requires the calculation to account for proof test coverage and for failures the test itself can cause.
The life-cycle framing is often credited to HSE’s Out of Control, which found poor specification behind 44% of the control system failures it studied. That study published in 1995, a decade after the ISA panel was commissioned, so it confirmed the committee’s direction rather than setting it.
Cybersecurity Joined the Safety Problem
Protective systems built on microprocessors and connected networks acquired an attack surface the hardwired systems they replaced did not have.
ISA formed its cybersecurity committee in 2002 and published the first standard in 2007, work that became the IEC 62443 series. It ran on an entirely separate track from functional safety for years.
IEC 61511:2016 requires a security risk assessment of the safety instrumented system and requires the design to be resilient against what that assessment finds. That is the point the two tracks joined.
A deliberate attack is a systematic cause, not a random failure, so it cannot be addressed by the probability calculations the rest of the discipline runs on. An attacker is not a Poisson process.
Where the History Gets Told Wrong
- Treating the sequence as causal. A named accident is credited with producing a named standard, when the committees were usually already working and the accident changed the argument rather than starting it.
- Assuming IEC 61508 came first. Practitioners routinely assume IEC 61511 was derived from it, when the process sector standard preceding both was ANSI/ISA-S84.01 in 1996.
- Reading European regulation as a response to the US. The Seveso Directive predates OSHA Process Safety Management by a decade.
- Crediting Three Mile Island with ASME NQA-1. NQA-1 was four years into development when the accident happened.
- Reading CIMAH as a response to Bhopal. It is dated the day after, and it implements a directive adopted two years earlier.
- Assuming the parallel industries borrowed from the process sector. Nuclear quality requirements predate the process sector standards entirely, and the safety integrity level itself came out of UK defence and regulatory work.
What Comes Next
IEC 61508 Edition 3 is at committee draft for vote, with parts circulated for ballot during 2025 and publication expected around 2027. IEC 61511 Edition 3 is under consideration with no published committee stage or date, so the process sector standard will likely trail its parent again, as it did the first time.
Cybersecurity is the most likely area of expansion, given how recently it entered the standard and how fast the threat changes.
Digitalisation of field devices, wireless instrumentation, and diagnostic data at volumes nobody anticipated all press on assumptions the current editions were built on.
A Timeline of Standards, Regulations, and Accidents
What follows is when the major things actually happened in our industry. Read down it and the tidy sequence falls apart. It is kind of a jumble, and that is the point.
- 1859: Drake well, Titusville, Pennsylvania.
- 1870: Standard Oil founded.
- 1880: ASME founded.
- 1896: NFPA founded.
- 1897: First National Electrical Code.
- 1905: Grover Shoe Factory boiler explosion, Brockton, Massachusetts. 58 dead.
- 1906: IEC founded.
- 1915: First ASME Boiler and Pressure Vessel Code published.
- 1920: NEC introduces “extra hazardous locations.”
- 1931: NEC introduces hazardous location Classes.
- 1945: ISA founded.
- 1968: Programmable logic controller specified; first units ship 1969.
- 1970: 10 CFR 50 Appendix B, nuclear quality assurance (US). HIMA Planar certified by TÜV.
- 1971: ANSI N45.2 nuclear quality assurance standard.
- 1974: Flixborough, UK. 28 dead.
- 1976: Seveso, Italy.
- 1979: Three Mile Island, US. ASME NQA-1 first issued, after four years in development.
- 1982: Seveso Directive.
- 1984: ISA Standards Panel 84 commissioned. Bhopal, India. CIMAH in the UK.
- 1985: IEC task group on generic programmable electronic systems standard.
- 1986: First certified programmable safety logic solvers.
- 1987: HSE guidance introduces a graded level of safety integrity.
- 1988: Piper Alpha, UK North Sea. 167 dead.
- 1989: Phillips Pasadena, US. 23 dead.
- 1991: UK Ministry of Defence interim standards publish numbered safety integrity levels.
- 1992: OSHA Process Safety Management rule.
- 1993: CCPS publishes Guidelines for Safe Automation of Chemical Processes, using SIS to mean safety interlock system.
- 1995: HSE publishes Out of Control.
- 1996: ANSI/ISA-S84.01 published. EPA Risk Management Program rule. Seveso II.
- 1998: IEC 61508 Parts 1, 3, 4 and 5 approved; Parts 2, 6 and 7 follow in 2000.
- 1999: COMAH replaces CIMAH in the UK. Final draft of IEC 61508-2 names IEC 61511 as the proposed process-sector implementation.
- 2001: IEC 61513 first edition for nuclear. CCPS publishes Layer of Protection Analysis.
- 2002: ISA forms its industrial cybersecurity committee.
- 2003: IEC 61511:2003 published.
- 2004: ANSI/ISA-84.00.01-2004 adopts IEC 61511 in the US.
- 2005: Texas City, US. Buncefield, UK.
- 2010: IEC 61508:2010 published. Deepwater Horizon, Gulf of Mexico.
- 2011: ISO 26262:2011 published.
- 2012: Seveso III.
- 2016: IEC 61511:2016 published.
- 2018: ANSI/ISA-61511 replaces the 84.00.01 designation.
Why This History Matters
We at SIL Safe are engineers, but we are also big fans of history. Naturally, we are interested in the history of our own profession.
Knowing the story behind a requirement changes how you apply it. A clause you understand the origin of is a clause you can argue about sensibly. A clause you only know the text of is one you either over-apply or wave away.
The practitioners who make good functional safety calls on hard problems are usually the ones who know why the standard says what it says, not just what it says.
This one took a lot of digging, and some of it sits in committee records and trade press that are hard to reach. We have done our best, but if we have something wrong, tell us and we will fix it.
Frequently Asked Questions
When were the three primary terms, safety instrumented system, safety instrumented function, and safety integrity, first written down in a formal document?
They arrived separately, and the oldest of them did not come from the process industry at all. Safety integrity as a graded concept came from HSE’s 1987 guidance on programmable electronic systems, and the first numbered levels appeared in the UK Ministry of Defence interim standards of 1991, on a scheme that differed from the one IEC later settled on. Safety instrumented system is first confirmed in ANSI/ISA-S84.01-1996, where it meant both a single loop and the whole system. Safety instrumented function did not arrive until IEC 61511:2003, which is what finally separated the loop from the system.
Was process safety earlier to use functional safety than the other industries that use functional safety?
Yes within the IEC 61508 family, no overall. The process sector got to functional safety first among the sector standards, well ahead of automotive in 2011 and machinery in 2005, and rail was developing alongside. But nuclear had enforceable quality requirements for safety-related work from 1970, long before any of it. That is not functional safety: it governs how work is controlled and documented, not whether a protective function achieves a required performance.
Someone on my team keeps saying they work to ISA 84. What does that actually mean now?
They are probably a little behind on how the standards evolved. It either means their plant is still running to a very old version, or they are misspeaking and what they are actually working to is the IEC 61511 version. There is no standalone S84 design standard anymore, so in practice almost everyone saying “ISA 84” means ANSI/ISA-61511, which is IEC 61511 as adopted in the US.
Why is there a separate standard for the process industry at all? Why can’t I just use IEC 61508?
Because the two standards split functional safety between different audiences. IEC 61508 is for the people who build and certify devices, and IEC 61511 is for the people who select those devices and put them together on a plant. You can read 61508 all day and still not know how to specify a SIF for your reactor. The process sector also got its own standard because its functions sit idle for years and are called on rarely, which is why probability of failure on demand governs there rather than a failure rate per hour.
How did anyone verify a SIL before certified devices existed?
Prior use and proven in use, built on the operating history at your own site. You argued from your own maintenance records that a device had performed acceptably in comparable service. It favoured big operators with long records and left everyone else guessing, which is a large part of why certified devices took over so completely once they were available. Prior use is still the only route for devices and services where no certified option exists.
Further Reading
From SIL Safe
- Functional Safety Is Not the Same as Occupational Safety
- Where Does the Data Come From? A Guide to Failure Rate Data Sources in Functional Safety
- Process Hazard Analysis (PHA) – One Term, Many Meanings
- Functional Safety Assessment (FSA) vs. Audit – What’s the Difference?
External resources
- The Evolution of Process Safety: Current Status and Future Direction
- The History of ASME’s Boiler and Pressure Vessel Code
- The Flixborough Disaster: Report of the Court of Inquiry
- Buncefield: Why did it happen?
- CSB Final Investigation Report, BP Texas City
- Seveso II: General Presentation and Explanation of Requirements
- ISA84 approves IEC 61511, moves ahead on key support documents
- Introduction and Revision of IEC 61508, Measurement and Control